Policy-as-Code for Terraform: Catch Cloud Misconfigurations Before They Ship
Scanning Terraform is easy. Making it a guardrail engineers trust is harder. Here is my two-layer pattern: Checkov for baselines, OPA for your own rules.
I help enterprise security, platform and DevOps teams secure their multi-cloud environments, combining cloud security architecture, Infrastructure-as-Code and AI applied to security.
What I do
Four areas, the tools I use most. The full skills matrix lives on the resume.
CNAPP architecture and compliance for multi-cloud and Kubernetes estates.
Security embedded in pipelines and cloud operations, as code.
Detection engineering, dashboards and automated response playbooks.
Where it started: NGFW, segmentation and secure access at scale.
Highlighted = expert level on the resume. Also: PHP / Laravel, JavaScript, MySQL for product work.
Now · November 2026
Leading cloud security engagements across EMEA, from discovery and Proof of Value to production.
Field notes on cloud threats, IaC and AI applied to security, on this blog.
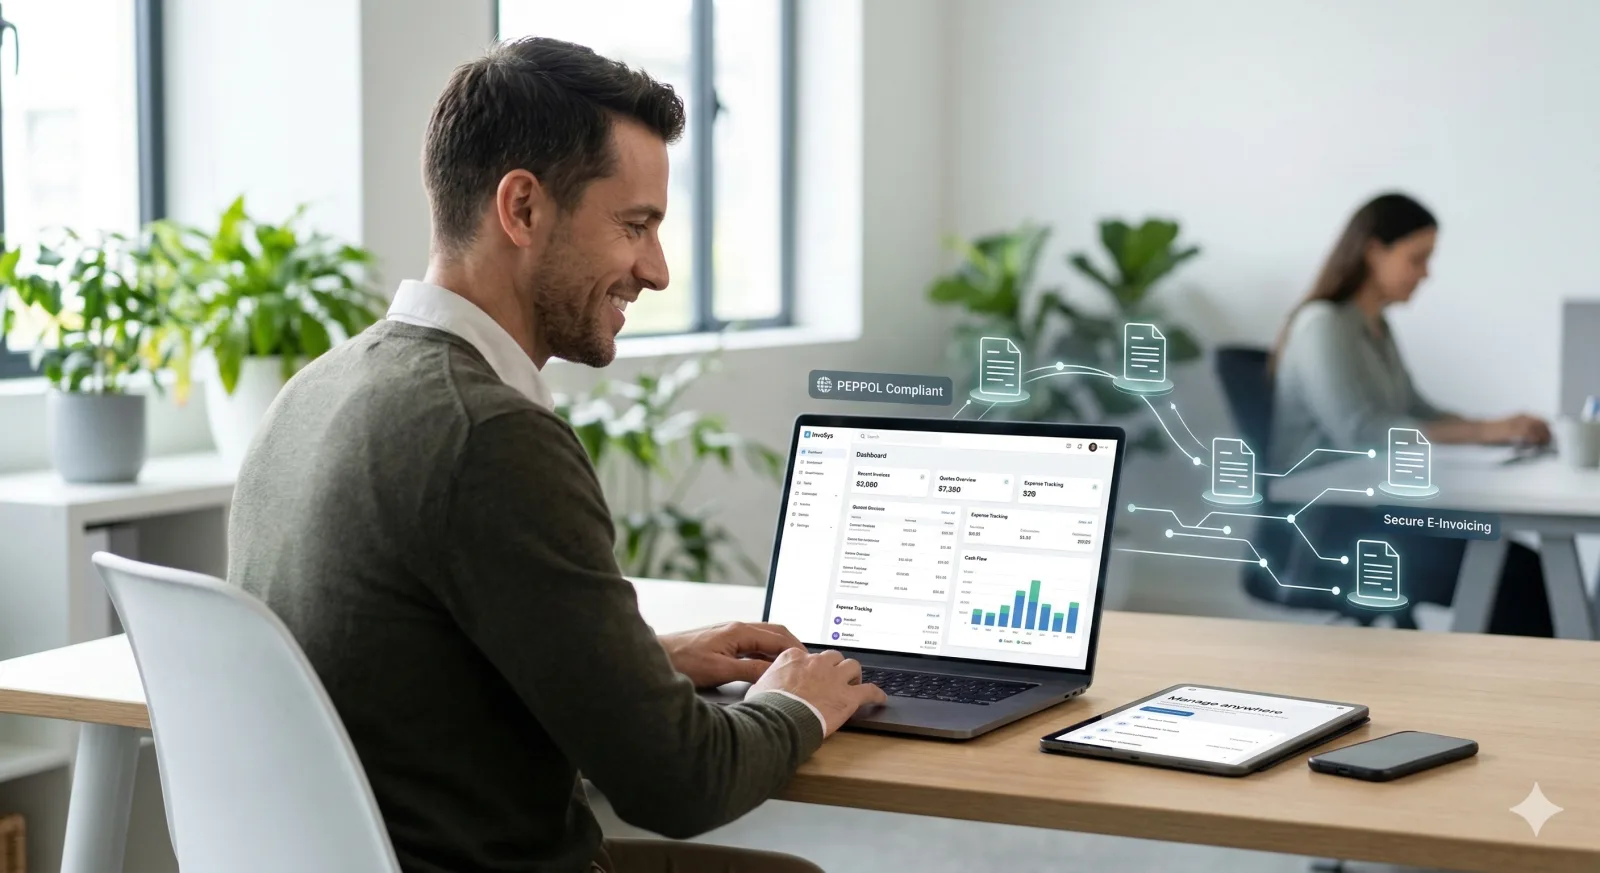
InvoSys: PEPPOL e-invoicing for Belgian freelancers and SMEs
Quotes, invoices, credit notes and expenses in one place, sent and received over the PEPPOL network.
In progress
Blog
Scanning Terraform is easy. Making it a guardrail engineers trust is harder. Here is my two-layer pattern: Checkov for baselines, OPA for your own rules.
Three documented cloud-threat cases, with sources: the September 2025 npm supply-chain attack, a campaign against exposed .env files, and DPRK-linked cryptocurrency theft.
Happy to talk architecture, Kubernetes security, Terraform or AI applied to security.